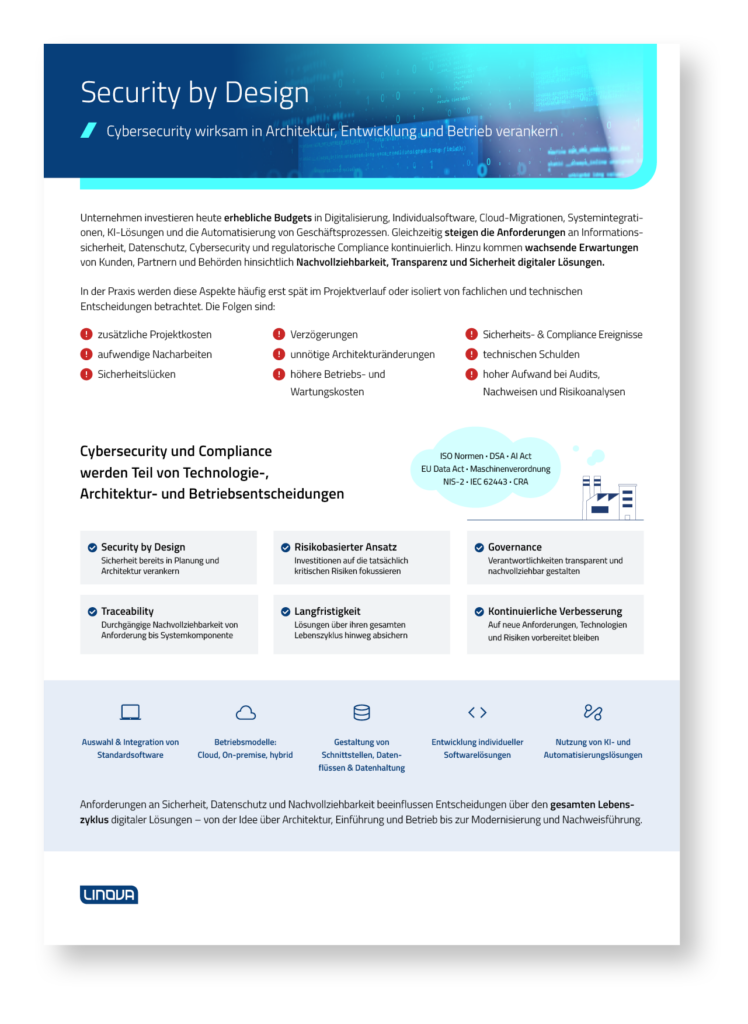
Security by Design

Effectively Embedding Cybersecurity in Architecture, Development, and Operations

Today, companies are investing significant budgets in digital transformation, custom software, cloud migrations, system integrations, AI solutions, and business process automation. At the same time, requirements for information security, data protection, cybersecurity, and regulatory compliance are constantly increasing. Added to this are growing expectations from customers, partners, and government agencies regarding traceability, transparency, and the security of digital solutions. In practice, these aspects are often not considered until late in the project or in isolation from business and technical decisions.

The consequences of a lack of security:

Additional project costs
Delays
Security & Compliance Incidents
Time-consuming rework
Unnecessary architectural changes
Technical debt
Security vulnerabilities
Higher operating and maintenance costs
Significant effort required for audits, compliance documentation, and risk analyses

Cybersecurity and Compliance as Part of Technology, Architecture, and Operations Decisions

Regardless of whether companies are affected by the GDPR, NIS2, the Cyber Resilience Act (CRA), the AI Act, customer requirements, or industry-specific regulations, the underlying requirements are evolving in a similar direction. For companies, this means that cybersecurity and compliance are increasingly becoming integral parts of technology, architecture, and operational decisions.

Bullet Point

Security by Design: Embedding Security in the Planning and Architecture Stages

Bullet Point

Risk-Based Approach: Focusing Investments on the Risks That Are Truly Critical

Bullet Point

Governance: Ensuring Responsibilities Are Transparent and Accountable

Bullet Point

Traceability: End-to-end traceability from requirements to system components

Bullet Point

Long-Term Perspective: Ensuring Solutions Throughout Their Entire Lifecycle

Bullet Point

Continuous Improvement: Staying Prepared for New Requirements, Technologies, and Risks

Security by Design – All the Information at a Glance.

Provide guidance, implement security and compliance: We help you answer the right questions before decisions turn into costly challenges. Together, we develop future-proof digital solutions tailored to your needs. Learn more:

Security, data protection, and traceability requirements influence decisions throughout the entire lifecycle of digital solutions.

Selection &
Integration of Off-the-Shelf Software
Operating Models:
Cloud, On-Premises, Hybrid
Design of Interfaces, Data Flows, and Data Storage
Development of Custom Software Solutions
Use of
AI and automation solutions
Using
AI and automation solutions

What Companies Need to Do Now​

NIS2 Obligations s of Management

Here you can find out which companies are affected by the directive, what NIS2 obligations management teams have, and how to prioritize measures.

NIS2 Obligations for Management

What Companies Need to Do Now​

Here you can find out which companies are affected by the directive, what NIS2 obligations management teams have, and how to prioritize measures.

Cybersecurity & Compliance by Design as an Integral Component

Provide guidance
What requirements and risks are relevant?
  • Systematically identify and document security, compliance, and operational requirements
  • Assess risks and internal and external conditions to enable informed decisions
  • Establish clear, coordinated requirements as the basis for selecting and implementing appropriate technology
Create a Target Image
What are the goals, and what is particularly important?
  • Systematically document and prioritize stakeholder requirements, business objectives, and the business case
  • Derive the target architecture and necessary security properties to evaluate technological options
  • Prepare well-founded technology decisions that are viable from a functional, technical, and economic perspective
Implementing Cybersecurity & Compliance
How can both be effectively implemented?
  • Implement requirements and standards in architecture, development, and operational processes
  • Ensure traceability and auditability through clear documentation, responsibilities, and control points
  • Focus on secure, compliant, and operationally viable solutions that are technically effective and organizationally sustainable
Further Develop Solutions
What new challenges, opportunities, and risks are there?
  • Continuously assess new requirements, threats, and regulatory developments
  • Review existing solutions for effectiveness, risks, and the need for adaptation, and prioritize improvements
  • Create future-proof systems and continuously refine security measures to ensure long-term resilience

Our Services

  • Security Requirements Engineering
    Derivation and Prioritization of Security, Data Protection, and Compliance Requirements
  • Threat Modeling & Risk Analysis
    Identification of threats, attack vectors, and protective measures at the architectural and process levels
  • Secure Architecture Design
    Evaluation of target architectures, integration patterns, interfaces, data flows, and operational models
  • Secure Development Lifecycle
    Integration of security checkpoints into agile development, DevOps, CI/CD, and release processes
  • Security Controls & Evidence Management
    Definition of verifiable measures, responsibilities, and evidence for operations, audits, and compliance
  • Governance & Operating Model
    Clarification of roles, decision-making paths, and handoffs between development, security, and operations

Benefits of Collaboration

Bullet Point

Make requirements, risks, and dependencies transparent

Bullet Point

Establishing a Basis for Decision-Making Rather Than Relying on Assumptions

Bullet Point

Creating Future-Proof Digital Solutions

Free of charge and with no obligation

Schedule an initial consultation now

Sandra von König will answer your personal questions, provide guidance, and give you a clear overview of the options and added value.

Sandra von König
Your contact person

Schedule an initial consultation now

Free of charge and with no obligation

Sandra von König answers your personal questions, provides orientation and gives you a clear overview of the possibilities and added value.

Sandra von König
Your contact person

Wie datengetrieben ist Ihre Produktion?

Mehr Transparenz, weniger Stillstand

Laden Sie sich jetzt kostenfrei das E-Paper Potenzialanalyse: Daten & KI herunter und machen Sie den 5-Minuten-Check:

✔️ 10 Fragen zur Einordnung des digitalen Reifegrads
✔️ individuelle Erfolgschancen und Ableitungen für Ihr Unternehmen
✔️ konkrete, priorisierte Maßnahmen je Reifegradstufe

Klingt spannend? Mehr erfahren.